Administering Quick Receivable
This guide covers user roles, permission sets, and day-to-day administration in Quick Receivable. It's written for the Salesforce admin or AR Admin responsible for keeping the org configured correctly as your team grows.
User Roles
| Role | Typical Responsibilities |
|---|---|
| Collector | Works assigned accounts, sends AR emails and reminders, places AI collection calls, logs promises to pay, flags disputes, applies payments |
| Supervisor or Manager | Configures dunning templates, manages credit policy and applications, assigns collectors, reviews reporting, broader configuration access |
Permission Sets and Licenses
- Assign the QR Permission Set to team members who manage accounts on a day-to-day basis, as well as users responsible for configuring dunning, credit policies, and reporting.

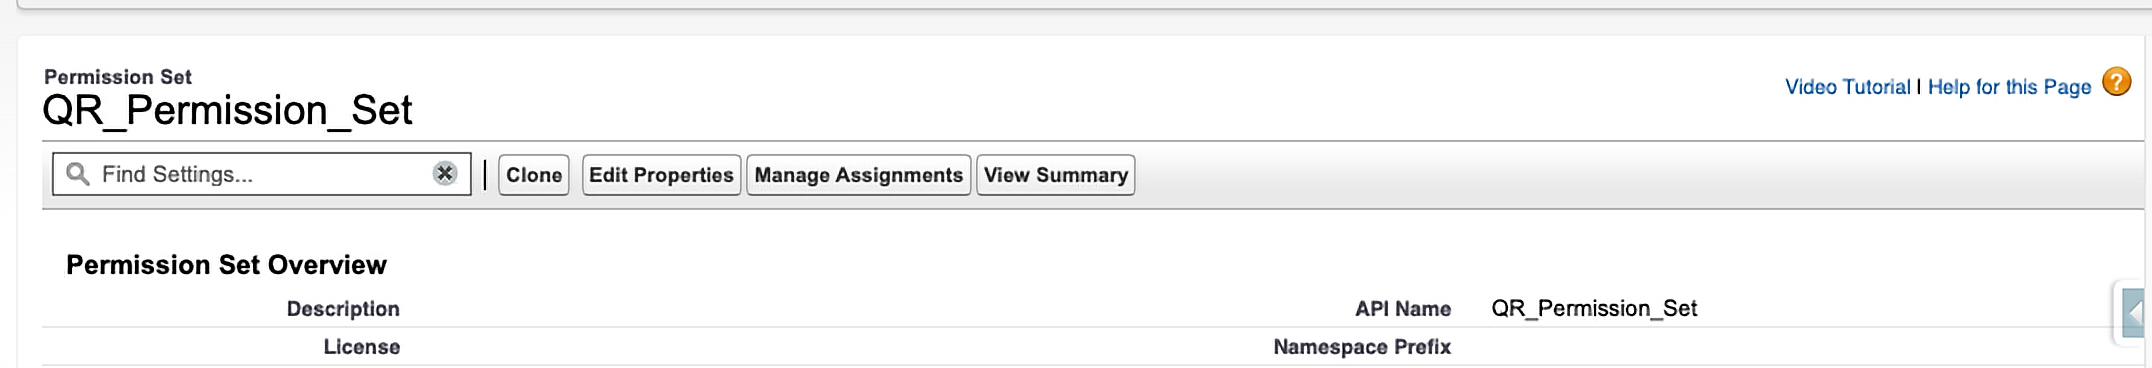
- Confirm each user has an active Salesforce license, since permission sets alone don't grant access without one.
Assigning Collectors to Accounts
- Open an account record and set the Collector field to assign ownership.
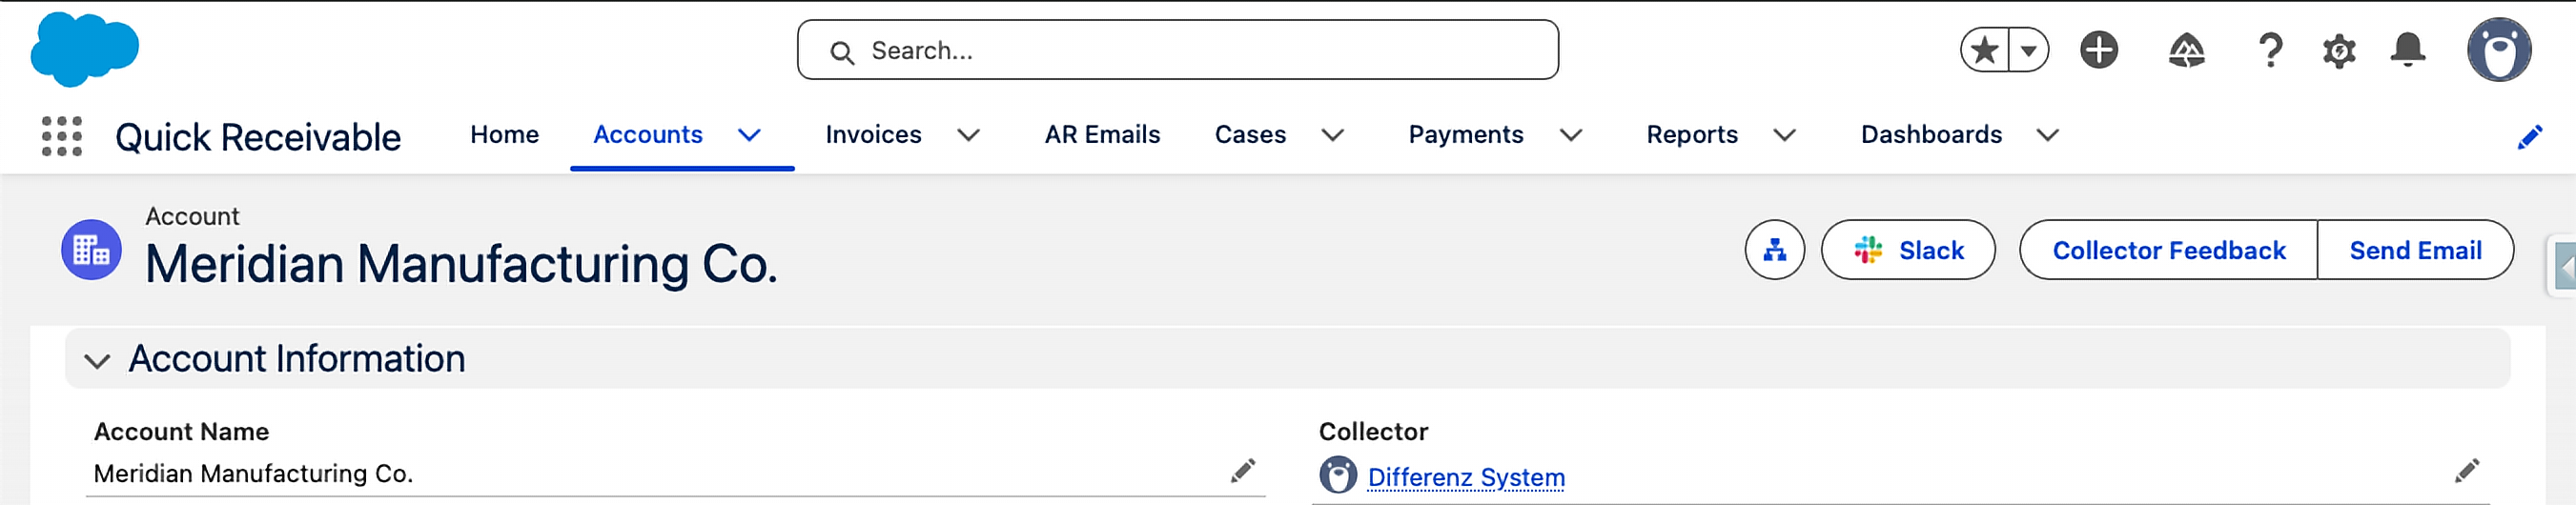
- For bulk assignment across many accounts, use a Salesforce list view mass-update or a data import to set the Collector field in one pass.
- Reassign accounts when a collector changes territory or leaves the team, so ownership never goes stale.
Managing Dunning Templates
AR Admins can edit the wording, timing, and tone of each stage in the reminder cycle (Early reminder, Due reminder, Past-due reminder, Final notice, and Broken-promise follow-up) from the Collections & Dunning configuration area. See Collections & Dunning for the full template list.
Security Model
Because Quick Receivable is Salesforce-native, it inherits Salesforce's standard security model rather than introducing a separate one.
- Access is controlled through permission sets and profiles, the same way any other Salesforce data is secured.
- Record-level access follows your org's existing sharing rules and ownership model.
- Single sign-on (SSO) and SAML, if your organization uses an external identity provider, are configured at the Salesforce org level.
Multi-Entity Considerations
If you operate multiple entities or subsidiaries, decide early whether they'll share one Quick Receivable instance with entity-level reporting, or whether they need separate collector pools and credit policies. Coordinate this with your implementation contact during the Implementation phase, since it affects how accounts, aging, and reporting are structured from the start.
Need help structuring roles for a larger team?
Reach us at info@quickreceivable.com or through our Contact Us page.
